
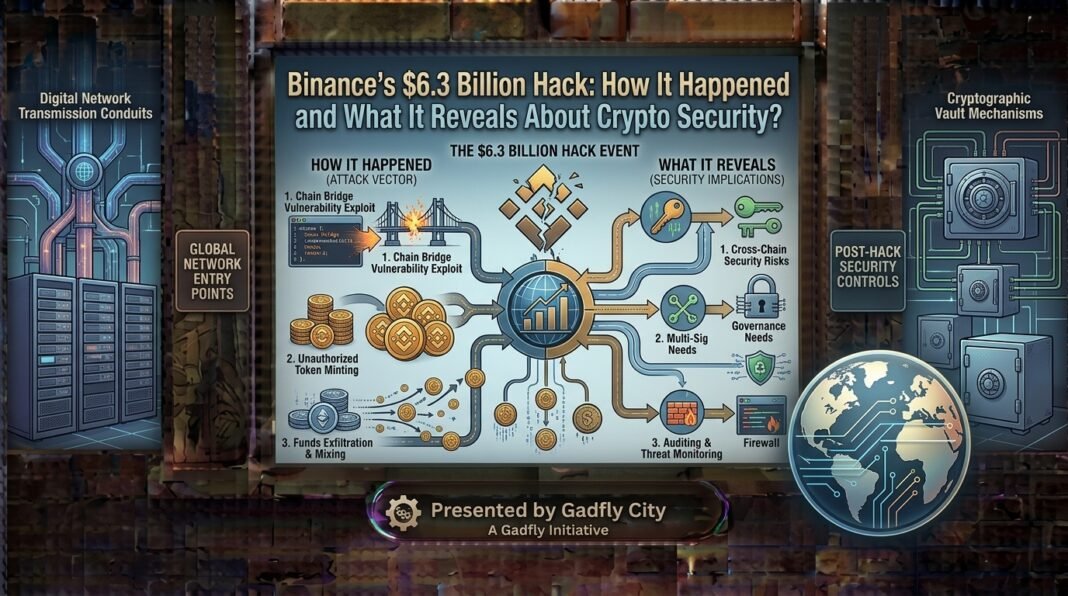
Hackers steal $6.3 billion from Binance on 2026-10-29 The attackers hacked into the employees’ devices and syphoned off some $6.34 billion in digital currency through the internal wallet infrastructure.The incident exposed serious weaknesses in crypto exchange security and demonstrated why even established platforms remain vulnerable, as explored by Gadfly City.
Key Takeaways
- The cryptocurrency assets involved were worth $6.34 billion, Binance said.
- Attackers allegedly used fake job interviews and malware to compromise employee devices.
- Authorisation of internal access and wallet transactions became a critical point of failure.
- The FBI said the attack was carried out by North Korean hackers who identified themselves as TraderTraitor.
- Binance said it had recovered 98% of the assets involved as of Nov. 3, 2026.
- Historical incidents with Mt. Gox and Ronin Network demonstrate similar vulnerabilities in crypto infrastructure.
- More robust control of access, independent security audits and safer wallet management are a must.
What went wrong in the $6.3B hack of Binance?
On 29 October 2026, Binance was hit by one of the biggest reported thefts of cryptocurrency in history. Hackers breached internal systems and carried out unauthorised trades from the exchange’s hot wallets.
According to Binance’s November 3 preliminary investigation report, approximately $6.34 billion in digital assets were affected. The company said it would absorb the financial impact rather than pass the losses to customers.
The FBI subsequently attributed the incident to North Korea, identifying the operation as TraderTraitor. However, North Korea has denied responsibility.
This distinction matters because cryptocurrency transactions are publicly traceable, but identifying the individuals or organisations controlling the wallets requires additional investigation.
Understanding the Attack: How Binance was Hacked
How the Binance Hack Happened As the investigation unfolds, it seems to be more complicated than a single compromised server or stolen password. Attackers reportedly took months to build access before getting to the exchange’s wallet infrastructure
1. Compromising of employee devices
Initial access was gained through malware and social engineering.
Binance said an employee downloaded a modified software package while trying to install an AI development tool. The company found the suspicious activity and swapped the compromised device, but the attackers had already gleaned information about the employee’s role and connections on the wallet infrastructure team.
Another employee was contacted through a genuine recruitment platform. The attackers built realistic identities, conducted fake job interviews and eventually talked the employee into downloading a malicious coding assignment.
The downloaded repo had malware that executed when installed.
The method shows how cryptocurrency cyberattacks are increasingly focusing on the person rather than trying to break into security systems directly.
2. Access to internal system
Attackers were able to access Binance’s internal environment using the compromised devices.
The attackers then used an internal AI tool to access the computers of more employees, the company’s preliminary report said.
They also obtained credentials and a token to deploy containers related to wallet infrastructure.
This is particularly important since development and operational permissions can provide access to sensitive systems, even if the attacker has not obtained the private key of the actual cryptocurrency wallet.
3. Wallet Transaction Authorisation Exploit
The attackers eventually reached the wallet-signing infrastructure and began executing unauthorised transactions.
Binance’s investigation mentioned an advanced transaction-authorisation technique that involved Ethereum’s EIP-7702 mechanism.
This Ethereum standard enables externally owned accounts to delegate code execution to another address through signed authorisations. The feature can improve wallet functionality, but improper or malicious authorisation can present serious security risks.
The attackers reportedly exploited this mechanism to establish unauthorised execution permissions over a hot wallet.
The important lesson is that private keys are not the only security boundary. Access to the systems that create, approve and execute transactions can also become a critical vulnerability.
Why Crypto Exchanges Remain Vulnerable
The Binance $6.3 Billion Hack highlights three areas where cryptocurrency platforms face considerable security challenges.
Hot Wallets and Private Keys
The hot wallets are still active. This allows exchanges to efficiently settle deposits and withdrawals.
But being always on line means you are more exposed to online attacks.
Cold wallets keep cryptocurrency offline, reducing the risk of internet threats. Keeping operating cash separate from longer term reserves reduces the impact of any one breach. All choices carry some risk.
Private keys are another challenge. If anyone gets enough control over a private key, or the signing process for it, they might be able to authorise transactions without the owner’s consent.
Smart Contract and Blockchain Bridges
Blockchain bridges enable transfer of assets and information across various networks. They are often based on intelligent contracts, validators and verification mechanisms.
Attackers can exploit any weakness in any of these components to manipulate transactions or make improper withdrawals of assets.
The October 2022 BNB Chain incident demonstrated this problem when attackers exploited a proof-verification vulnerability in the BSC Token Hub bridge and withdrew approximately two million BNB.
Employee Access And Software Supply Chains
The Binance incident also demonstrates why employee devices deserve the same attention as wallet infrastructure.
A compromised laptop, malicious software update or stolen deployment credential can provide attackers with access to systems that should otherwise remain isolated.
Security is more than just password protection. This involves restricting permissions, monitoring for any unusual activity and verifying any installation of sensitive software.
Binance Vs Other Biggest Crypto Hacks
Binance $6.3 Billion Hack is not an isolated incident. Past breaches of cryptocurrencies have shown how weaknesses in exchanges, bridges and decentralised applications can cause large financial losses.
| Event | Year | Declared worth | Major security flaw |
| Mt. Gox . | 2014 | $450 million back then | security and operational failures at the exchange |
| Binance | 2026 | There was $6.34 billion at stake. | Compromise of employee and purse authorisation |
| Ronin Network. | 2022 | Some $625 million | Validator access hijacked |
| Bridge BNB Chain | 2022 | BNB was worth some $570 million at the time | Cross-chain proof checking |
The figures are approximate and are historical figures, not direct comparable measures of ultimate financial loss.
Mt. Gox: The Flaws in Exchange Security
The collapse of Mt. Gox remains one of the biggest events in crypto history.
In 2014 the exchange filed for bankruptcy and suspended trading, saying some 850,000 Bitcoin had vanished, including customer holdings.
The incident was a long series of security and operational failures. Unlike the Binance $6.3 Billion Hack, the full causes can’t be reduced to a single, well-known technical exploit.
It showed that the reputation and market position of an exchange do not automatically ensure the safety of customer assets.
Ronin Network: The risk of access to centralised validators
March 2022 saw attackers compromise five of the nine validator keys used by the Ronin Network bridge.
This gave them sufficient control to approve fraudulent withdrawals involving approximately 173,600 ETH and 25.5 million USDC.
The incident exposed a fundamental weakness in bridge security: a system may be described as decentralised while depending on a relatively small group of validators.
BNB Chain: Bridge Verifier Failure
In October 2022, attackers exploited a vulnerability in the proof of verification process of the BSC Token Hub bridge.
About two million BNB were withdrawn before validators managed to freeze the chain temporarily.
This incident is different from the $6.3 Billion Binance hack that targeted employee devices and internal exchange infrastructure, instead targeting a blockchain bridge.
The cases above illustrate that cryptocurrency security failures can originate in very different parts of the tech stack.
What The $6.3 Billion Binance Hack Means For The Future Of Crypto Security
The incident is a case study in many practical lessons for cryptocurrency exchanges and investors.
First, exchanges need strict separation between employee devices, development environments and wallet infrastructure. Access to one system should never automatically provide access to another.
Secondly, sensitive transactions must be supported by independent approvals, spending limits and behavioural monitoring. Automated systems should detect unusual withdrawal patterns before large sums of cryptocurrency are withdrawn from the platform.
Third, exchanges should conduct regular independent audits and controlled penetration tests of their security.
The lesson is just as important for individual investors, too. Strong passwords, hardware security keys, withdrawal address verification and secure wallet practices may reduce exposure to account-level attacks.
These concerns also connect with broader discussions about technology infrastructure and financial risk. Just as the economic impact of the Iran War illustrates how disruptions can spread through interconnected markets, a major cryptocurrency breach can affect exchanges, investors and businesses beyond the original incident.
Similarly, the expansion of AI data centers raises wider questions about securing the computing infrastructure that increasingly supports financial and digital services.
Did Binance Recover the Stolen Crypto?
Binance’s response makes an important distinction between recovering stolen assets and replacing customer losses.
In a report on Nov. 3, 2026, Binance said it had restored about 98% of the affected token assets using company funds. It also reported some $2.85 billion of assets had been frozen or intercepted.
These are numbers for different processes. Replenishment is the replacement of the affected assets with company funds, and freezing is to prevent attackers from moving or spending assets under investigation.
The company also announced plans for an independent cybersecurity review and additional improvements to wallet controls, employee device protection and behavioural monitoring.
But restoring customer balances does not necessarily mean that the stolen cryptocurrency has been recovered in its original form.
Final Thoughts: Is Cryptocurrency Secure Enough?
The $6.3 Billion Binance Hack: A Hard Lesson on Crypto Storage Security The Binance $6.3 Billion Hack: The Hard Truth of Blockchain Transparency
Transactions can be publicly recorded, but the systems that control those transactions can still be compromised by human error, malicious software and poor isolation of permissions.
And as comparison with Mt. Gox, Ronin Network and BNB Chain shows, underlying weaknesses have changed over time. But the core problem remains similar: too much trust in systems that do not have sufficient independent safeguards.
Security has to be built into the foundation and not something you fix after a breach, as the industry evolves. Ultimately, though, the fate of cryptocurrency will be decided not only by the pace of development of digital finance, but also by how responsibly its infrastructure is safeguarded.
Frequently Asked Questions
1. What Is The Binance $6.3 Billion Hack?
On October 29, 2026, a major cryptocurrency security incident took place with the $6.3 Billion Binance hack. They hacked their way into internal systems and authorised the unauthorised transactions of around $6.34 billion worth of digital property.
2. How did the hackers get into Binance?
Binance’s initial investigation found attackers used fake recruitment interviews, malware, compromised employee devices and stolen internal credentials to access sensitive wallet infrastructure and carry out unauthorised transactions.
3. Who hacked binance?
The FBI said the October 2026 attack was carried out by North Korean state-sponsored hackers known as TraderTraitor. North Korea denied any responsibility. The investigation remains open for further developments.
4. Did Binance lose customers’ money?
Binance said it would absorb the financial impact of the incident. In its November 3 report, it said about 98% of affected token assets had been replaced using company resources.
5. Is Binance Secure to Use After the Hack?
Binance said it was rebuilding affected systems, replacing compromised devices and strengthening security controls. However, users should evaluate exchange risks on their own and should not view any centralised platform as being entirely risk-free.
6. Before Binance, what was the biggest crypto hack?
Some of the biggest attacks in history included the Ronin Network bridge attack in 2022 and other big breaches. Mt. Gox is also a landmark exchange failure, involving some 850,000 Bitcoin that went missing.
Stay Informed With Gadfly City
At Gadfly City, we believe understanding major financial and technological developments requires more than following headlines. We examine the underlying events, explain their wider consequences and connect complex issues with the decisions that affect everyday readers. Explore Gadfly City for more independent perspectives on cryptocurrency, technology, economics and global affairs.
Sources And References
- Binance – October 29, 2026 Security Incident: Initial Findings And Response Update
- FBI – North Korea Responsible For $6 Billion+ Binance Attack
- Ethereum Improvement Proposals – EIP-7702: Set Code For EOAs
- U.S. Department Of Justice – Ronin Network Cryptocurrency Hack Investigation
- U.S. Securities And Exchange Commission – Historical Cryptocurrency Exchange And Mt. Gox Filing
- BNB Chain – October 2022 Ecosystem Security Incident Update
- Ronin Network – Bridge Security Incident And User Fund Recovery